Tag
security
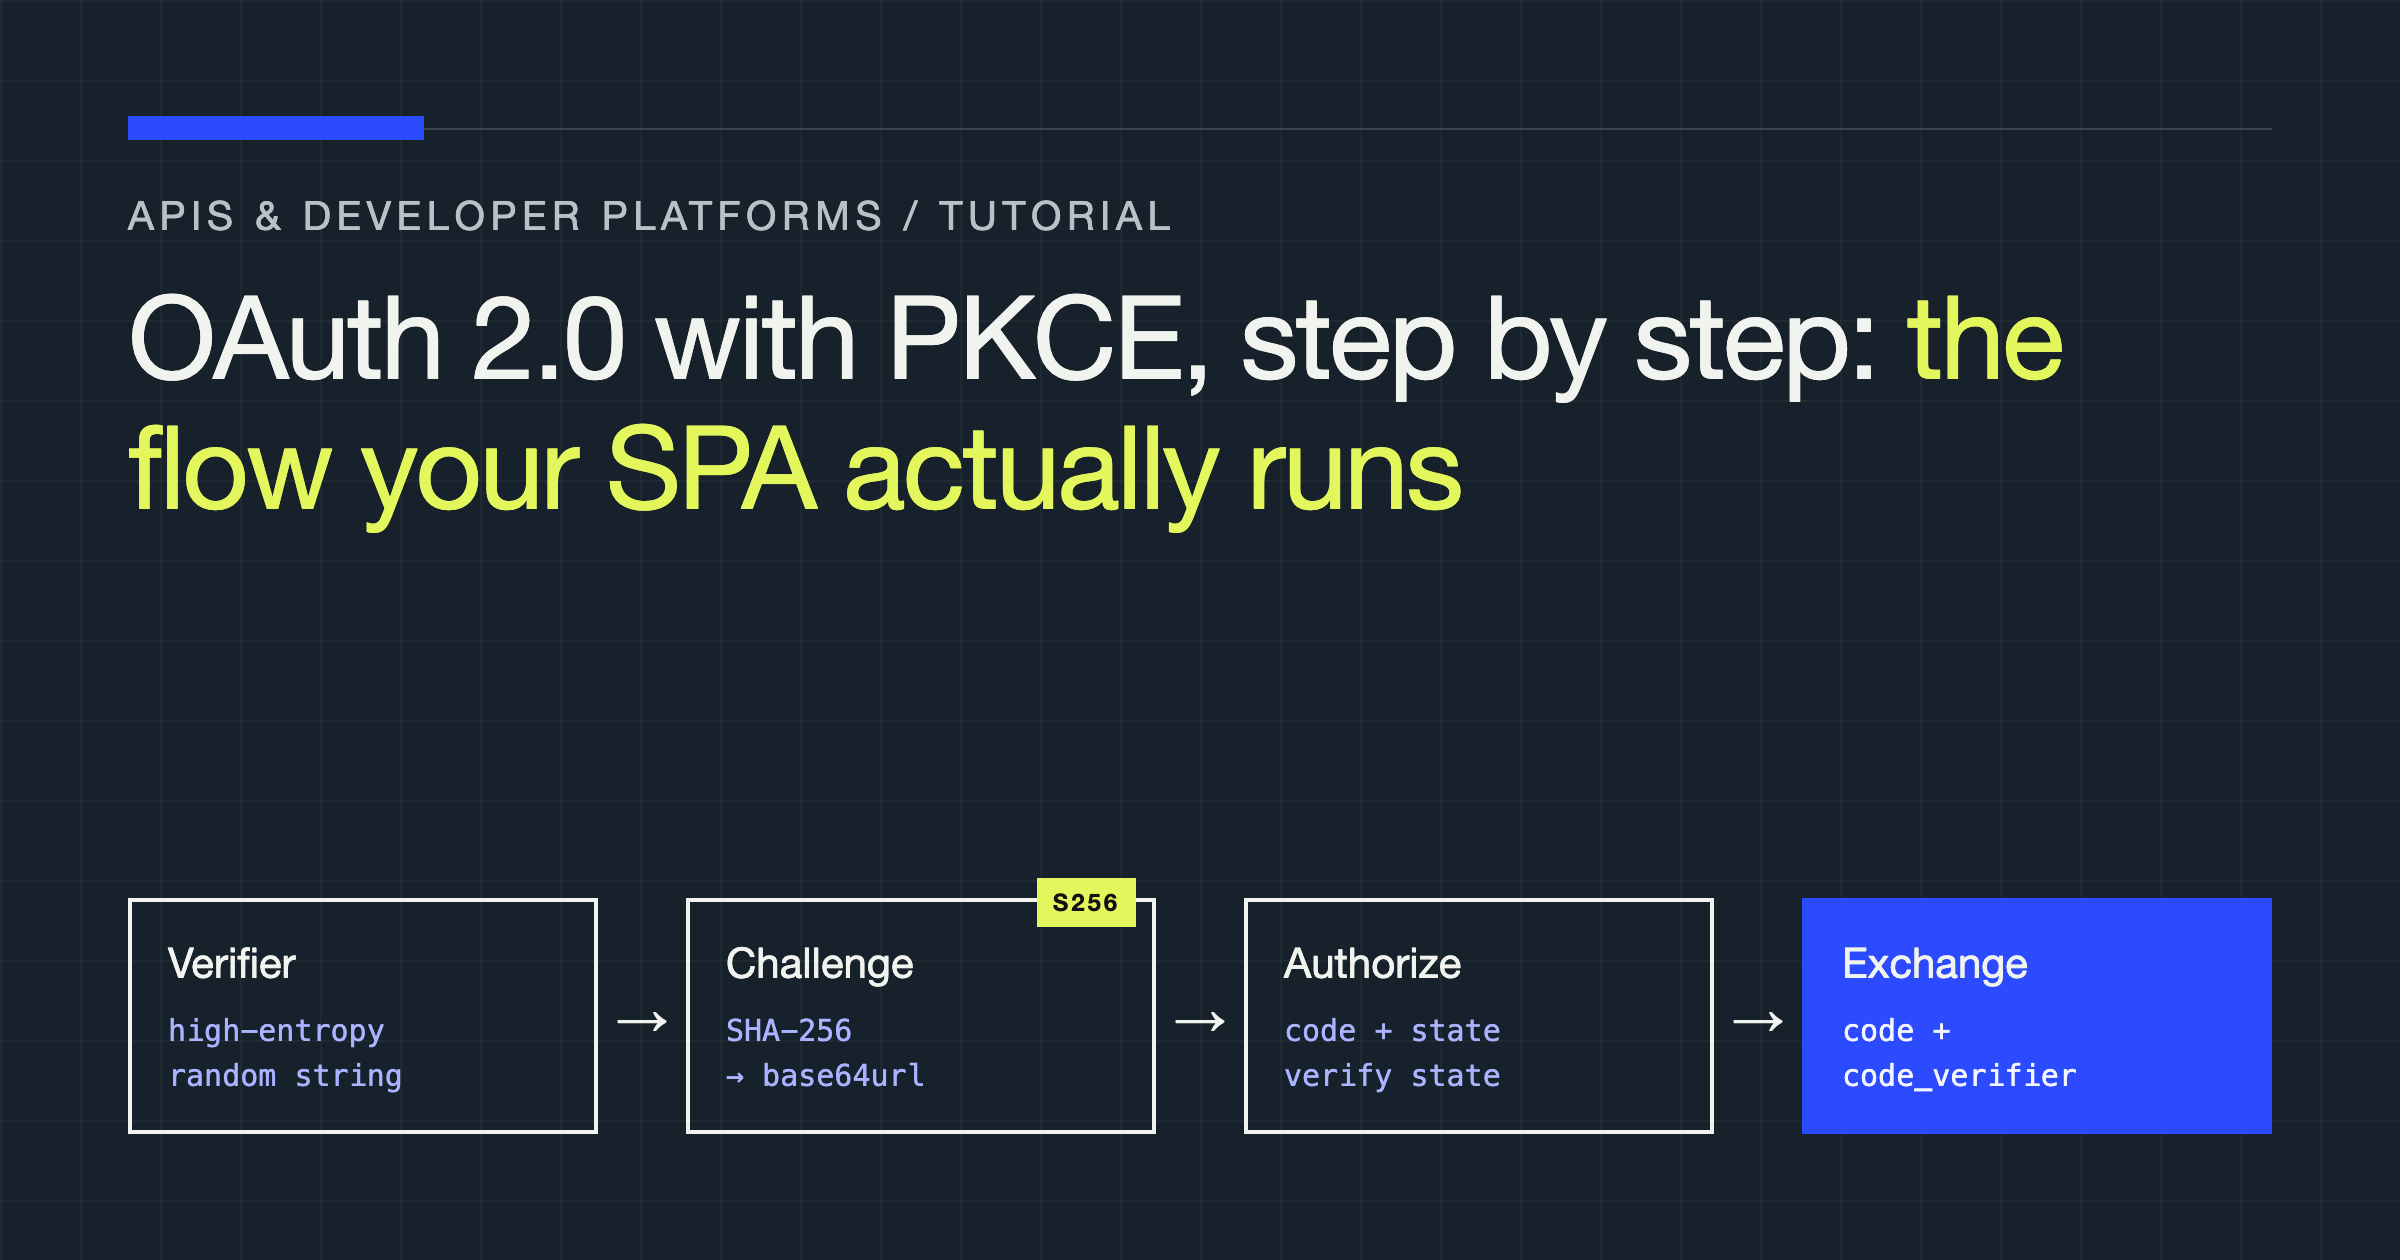
OAuth 2.0 with PKCE, Step by Step: The Flow Your SPA Actually Runs
Walk the authorization code flow with PKCE exactly as a browser app runs it, including the verifier math, state checks, and token storage decisions.
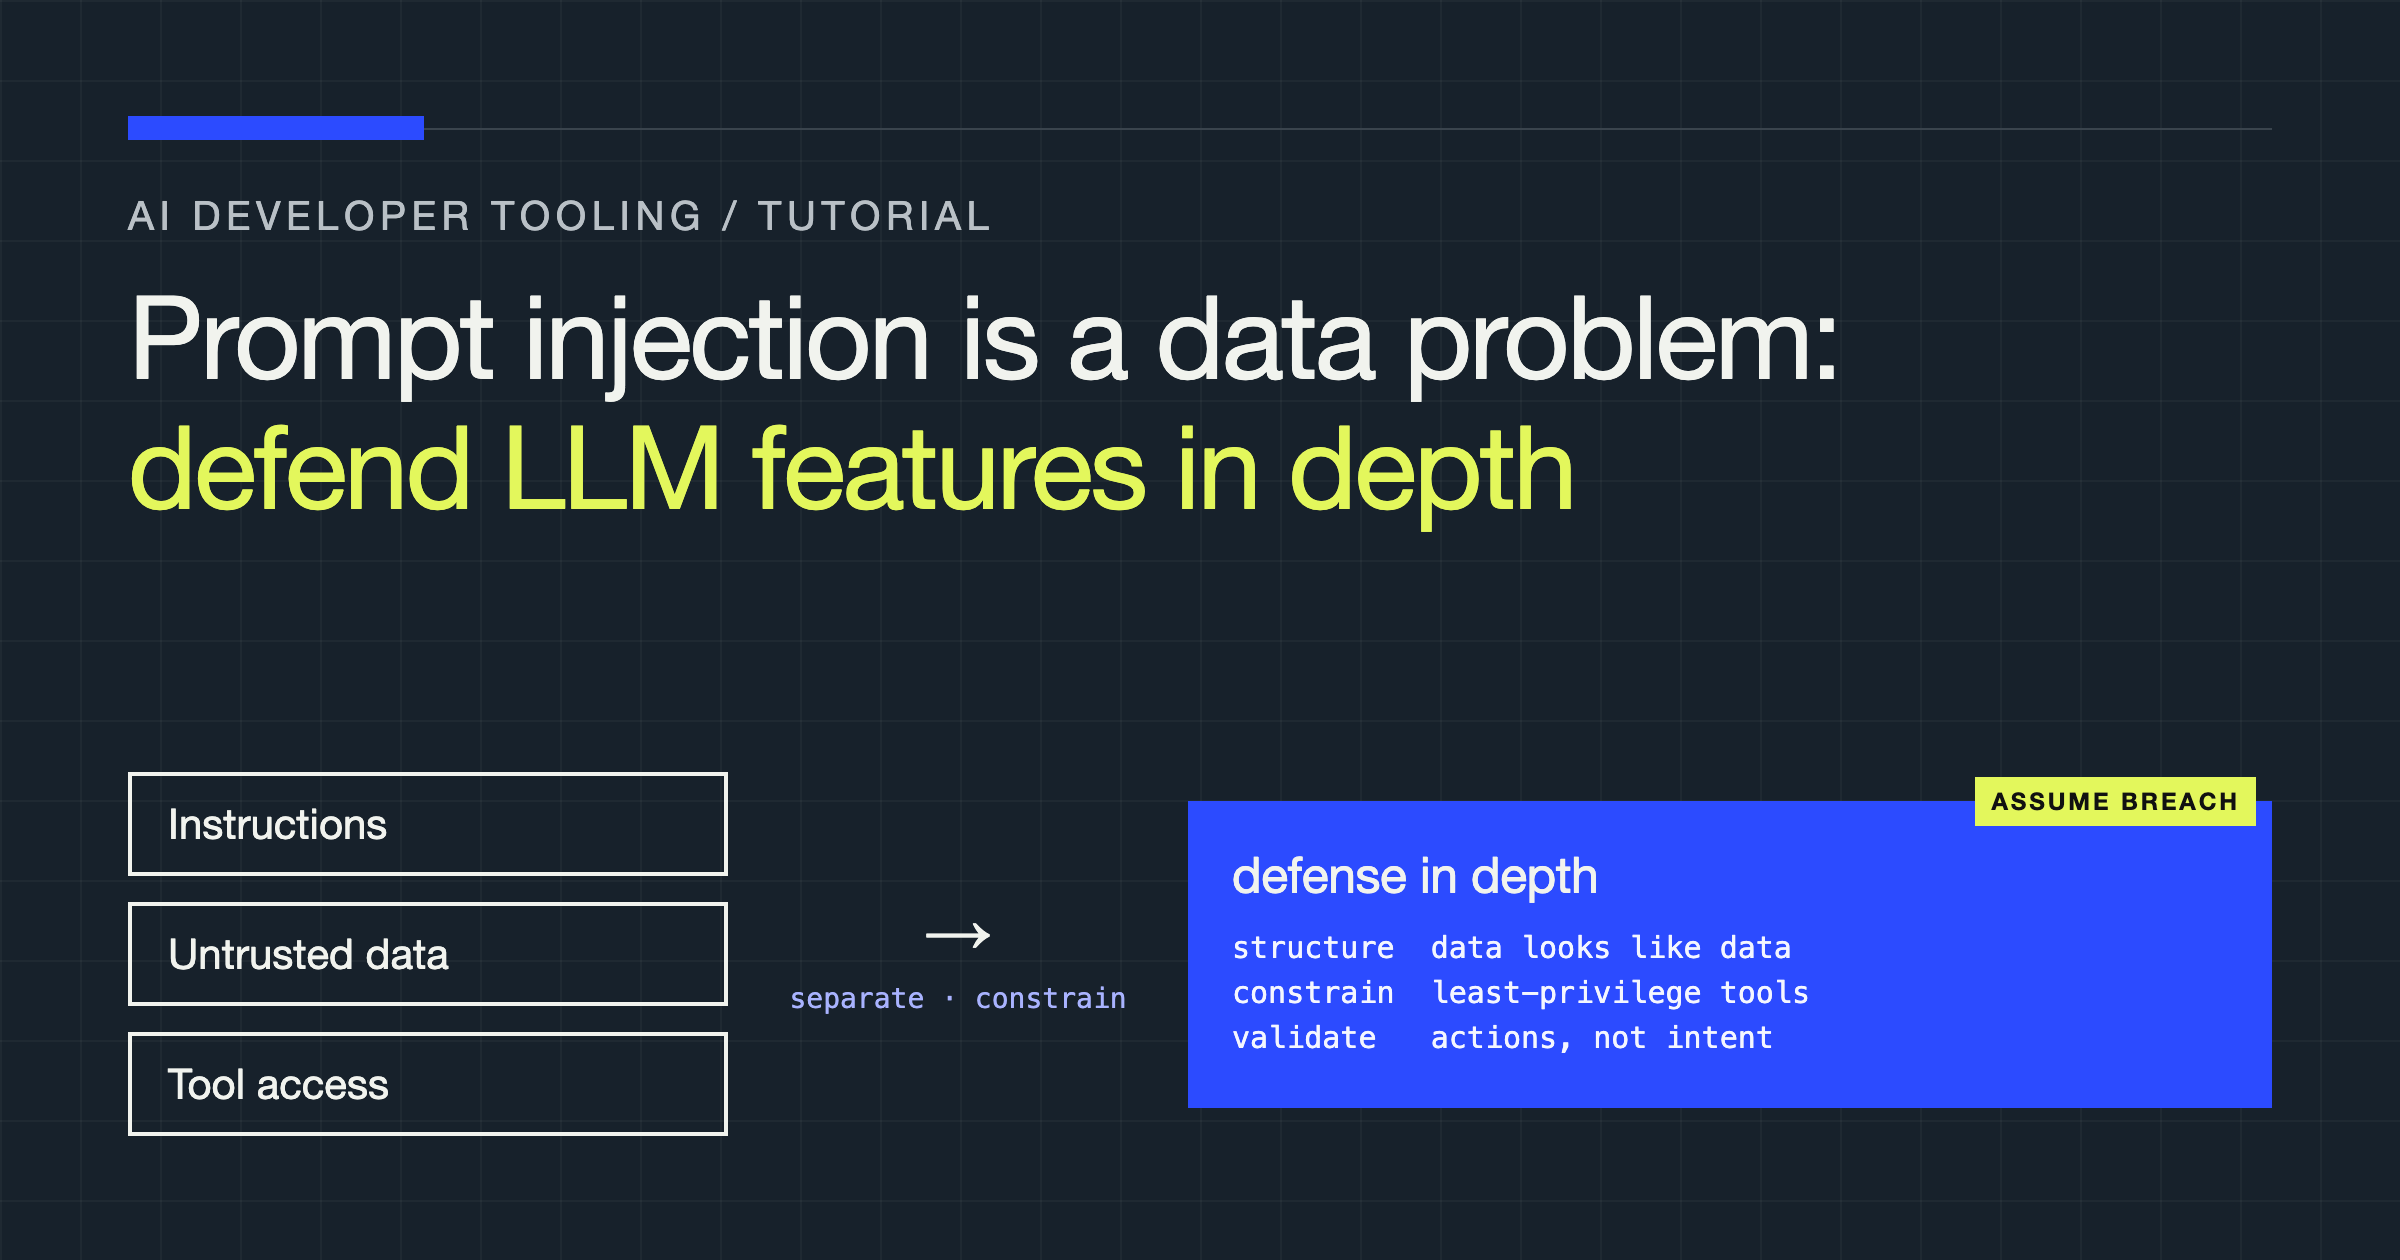
Prompt Injection Is a Data Problem: Defending LLM Features in Production
Prompt injection works because models cannot tell instructions from data. Defend in depth: separate the two, constrain tools, validate actions, and assume breach.
No matches in this set.
Clear a filter or try another combination.