Tag
api-design
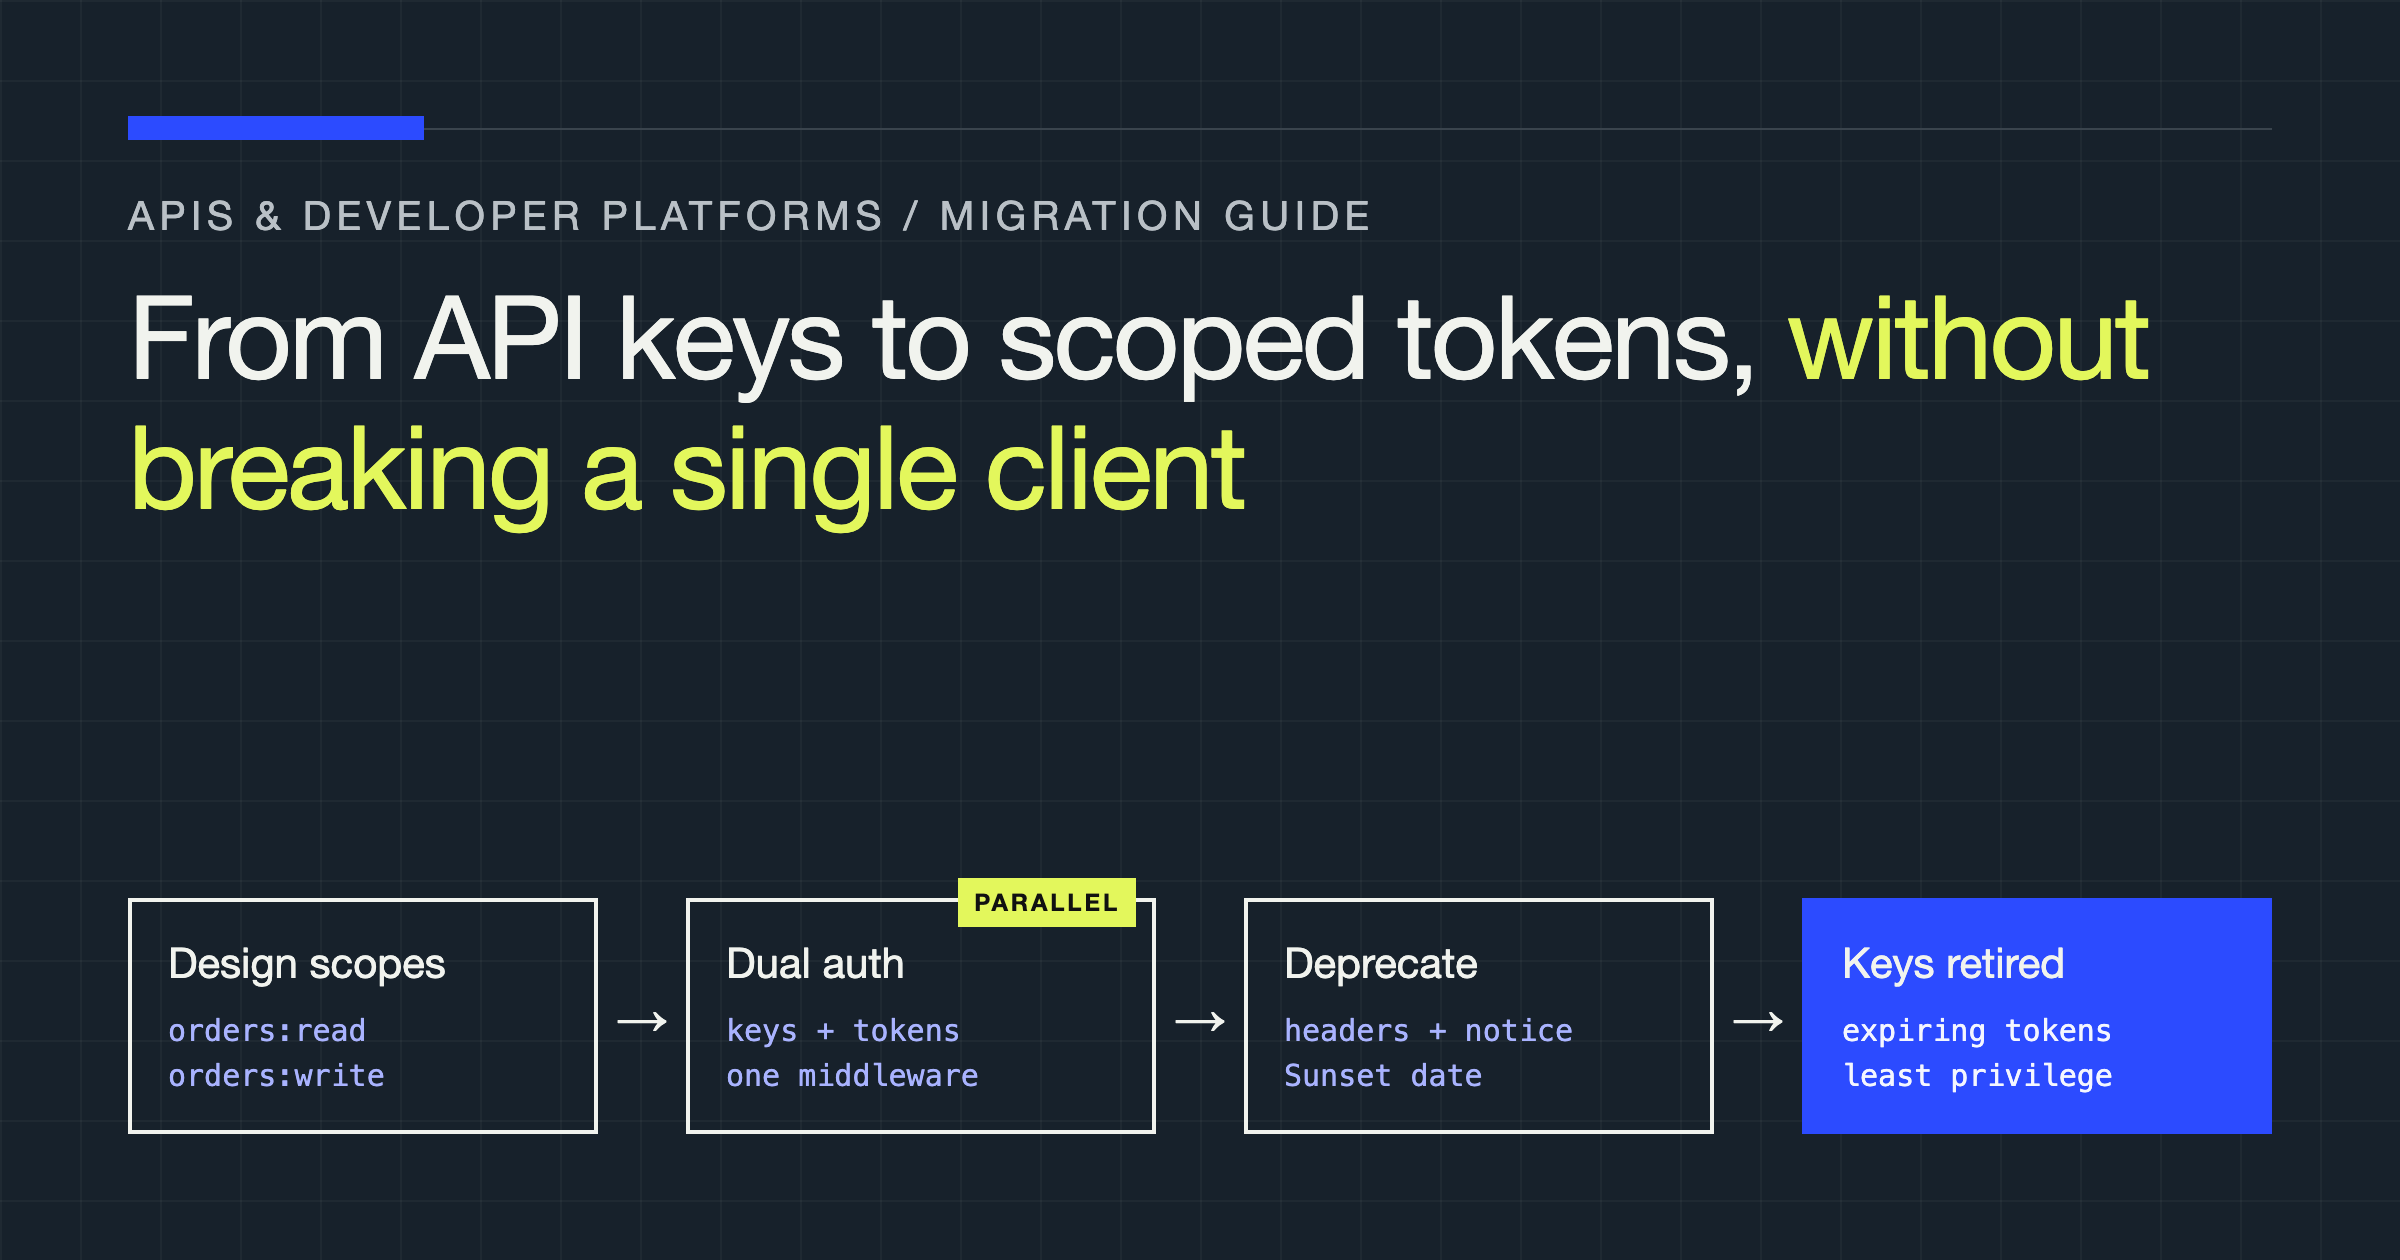
From API Keys to Scoped Tokens: Upgrading a Public API's Auth Without Breaking Clients
Migrate a public API from all-powerful API keys to scoped, expiring tokens: design the scopes, run both systems in parallel, and deprecate keys without breaking clients.
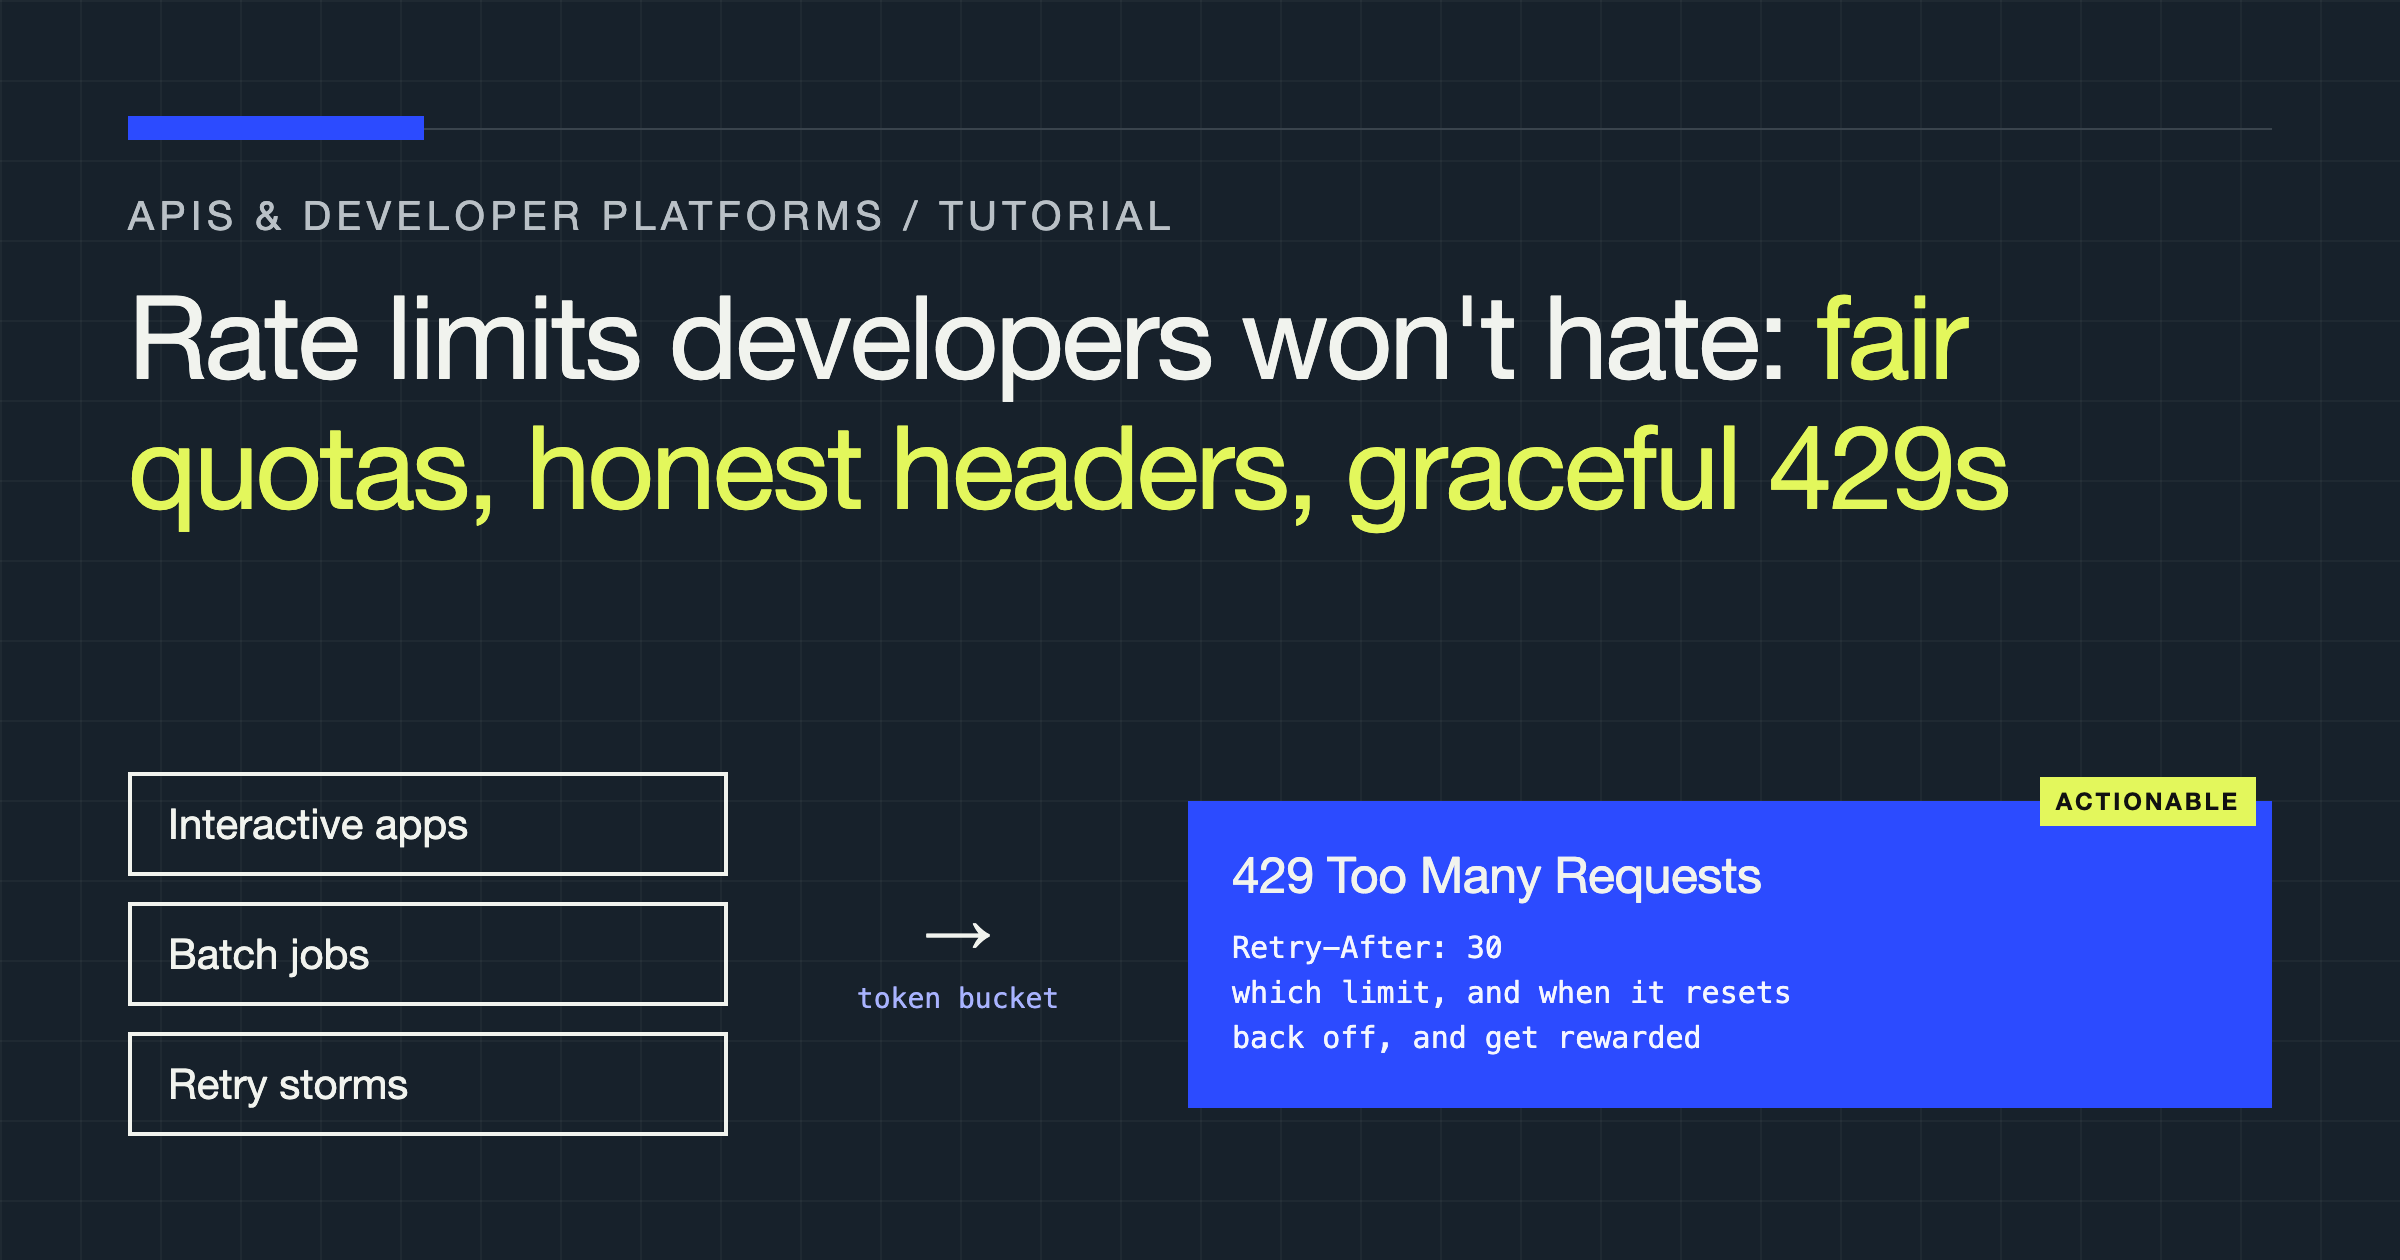
Designing Rate Limits Developers Won't Hate: Quotas, Headers, and Graceful 429s
Design rate limits that protect your API without punishing good clients: fair quotas, honest headers, and 429 responses developers can act on.
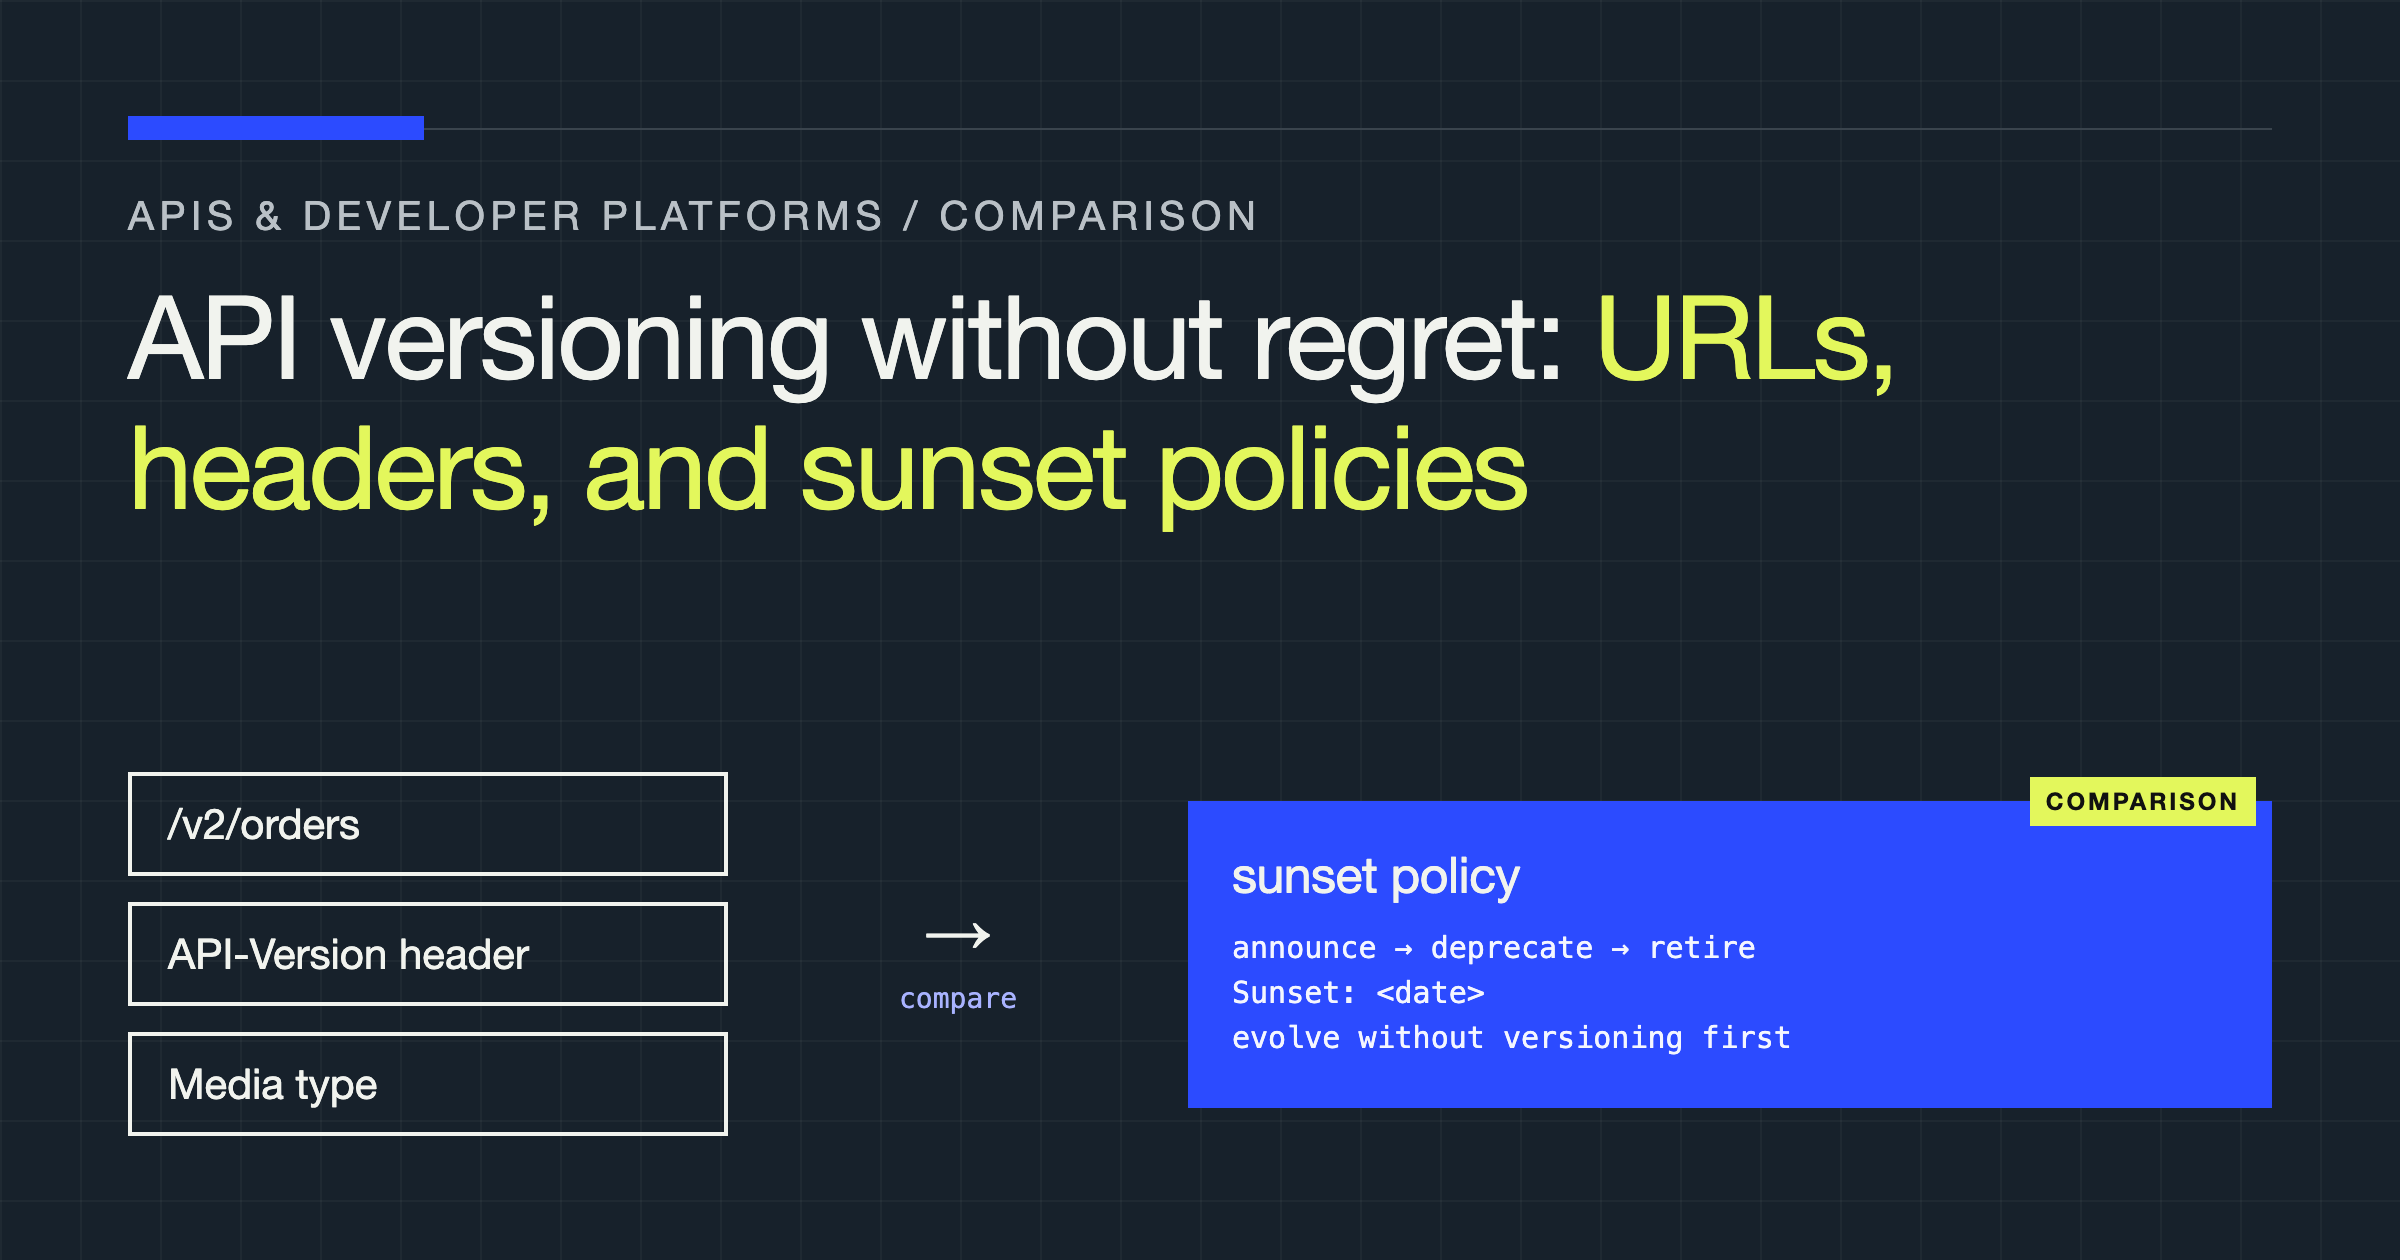
API Versioning Without Regret: URLs, Headers, and Sunset Policies Compared
Compare URL, header, and media-type versioning on real tradeoffs, and design a sunset policy that retires old versions without breaking clients.
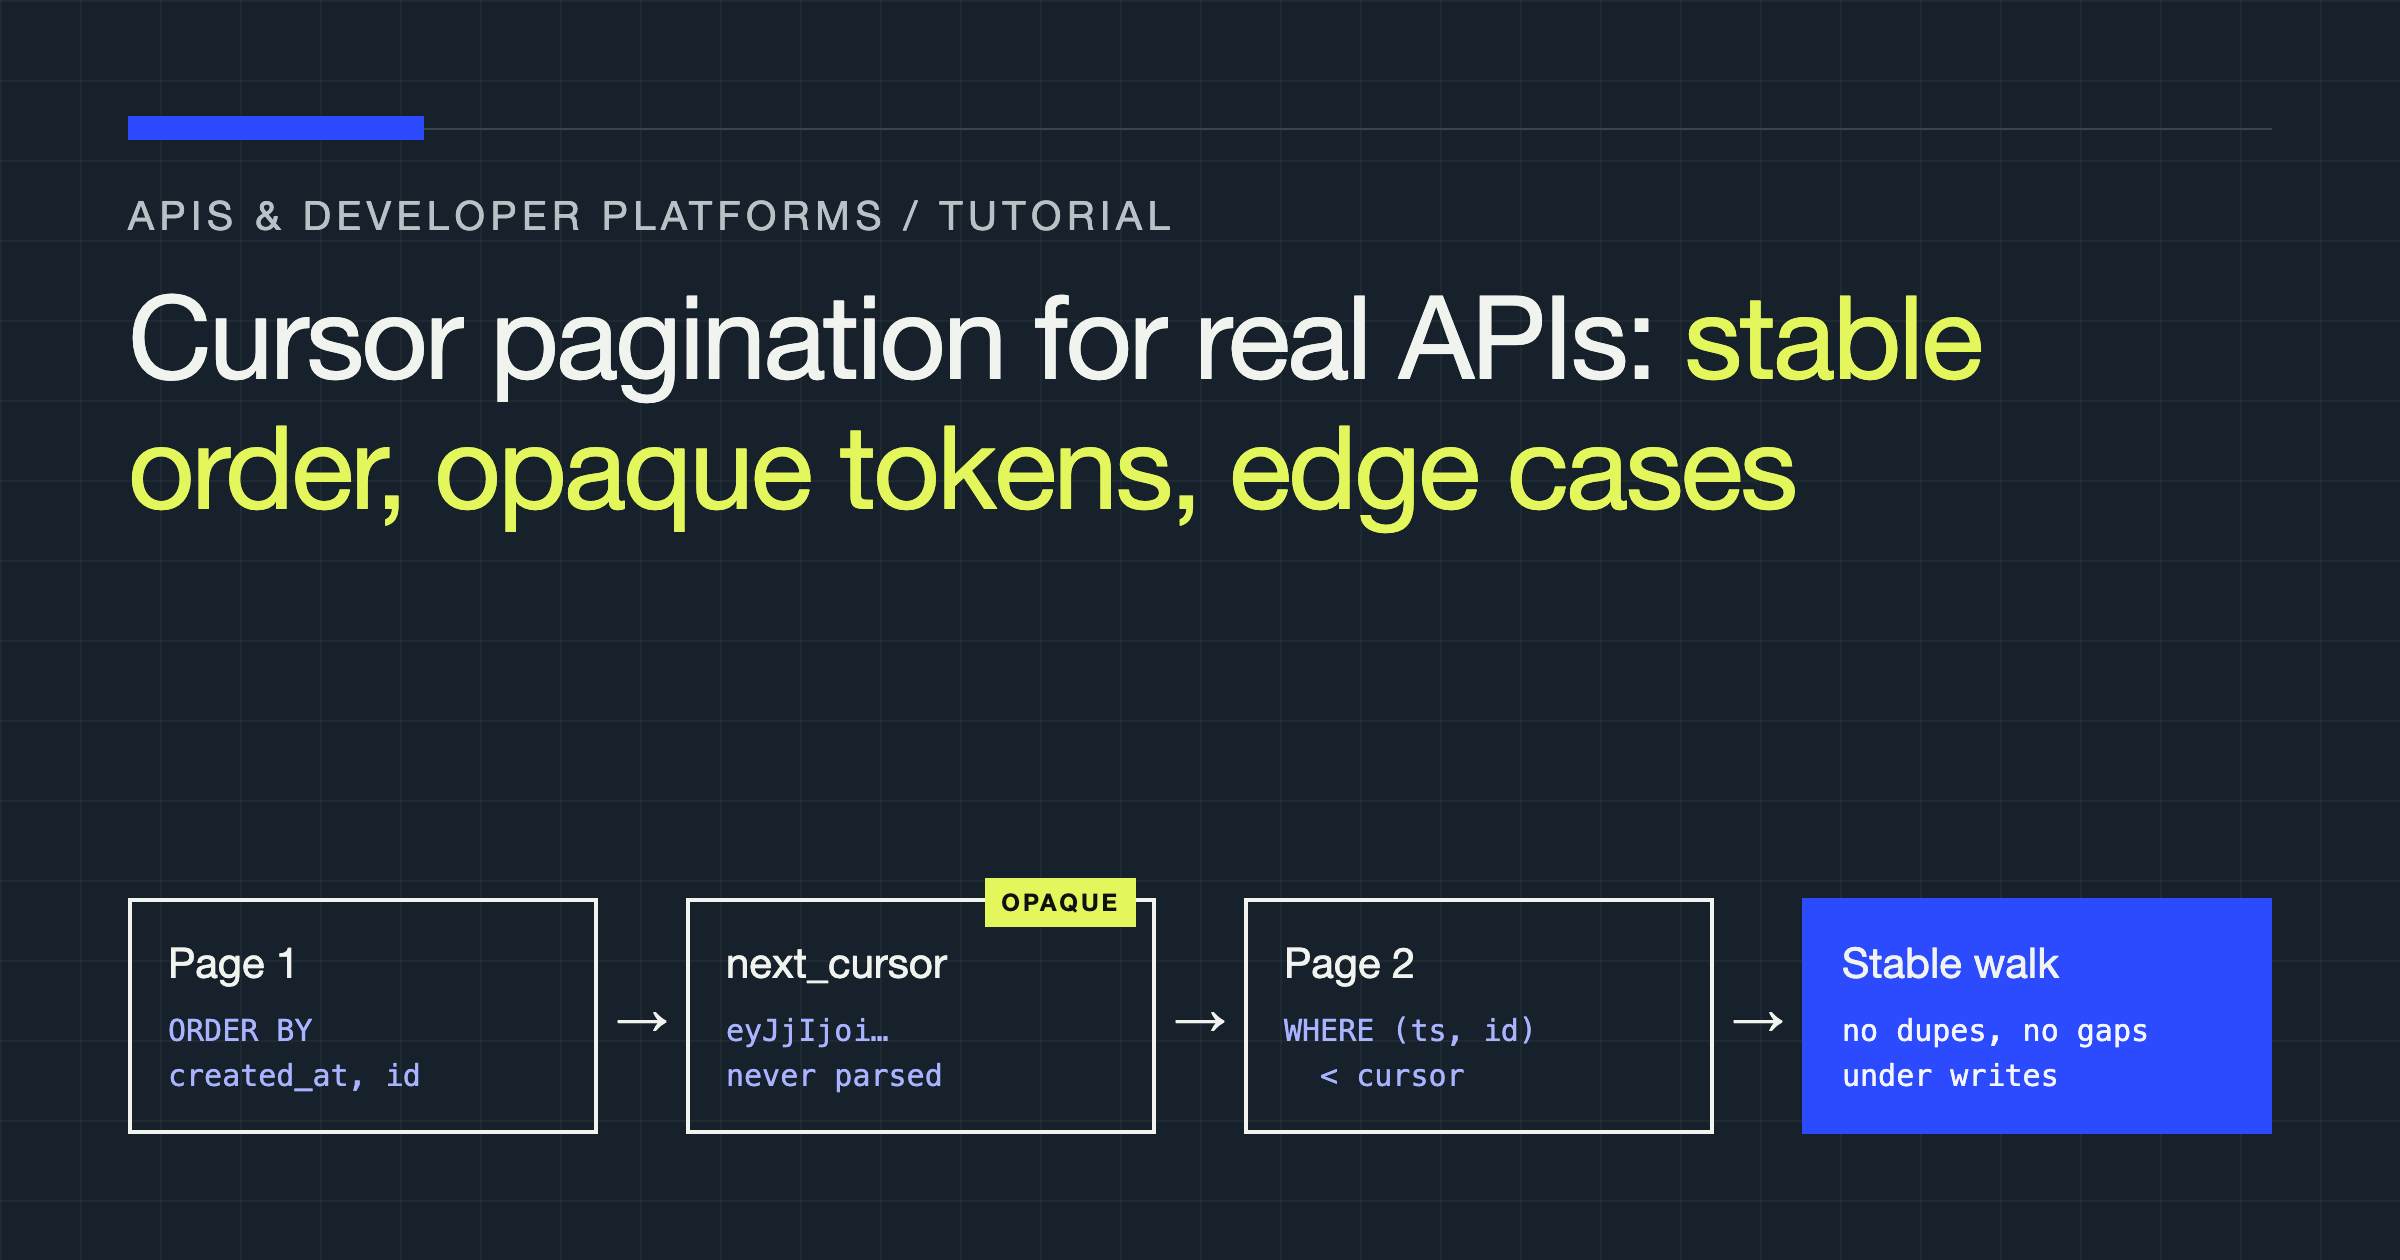
Cursor Pagination for Real APIs: Ordering Guarantees, Opaque Tokens, and Edge Cases
Implement cursor pagination that stays correct under inserts and deletes, with stable ordering, opaque tokens, and honest handling of filters.
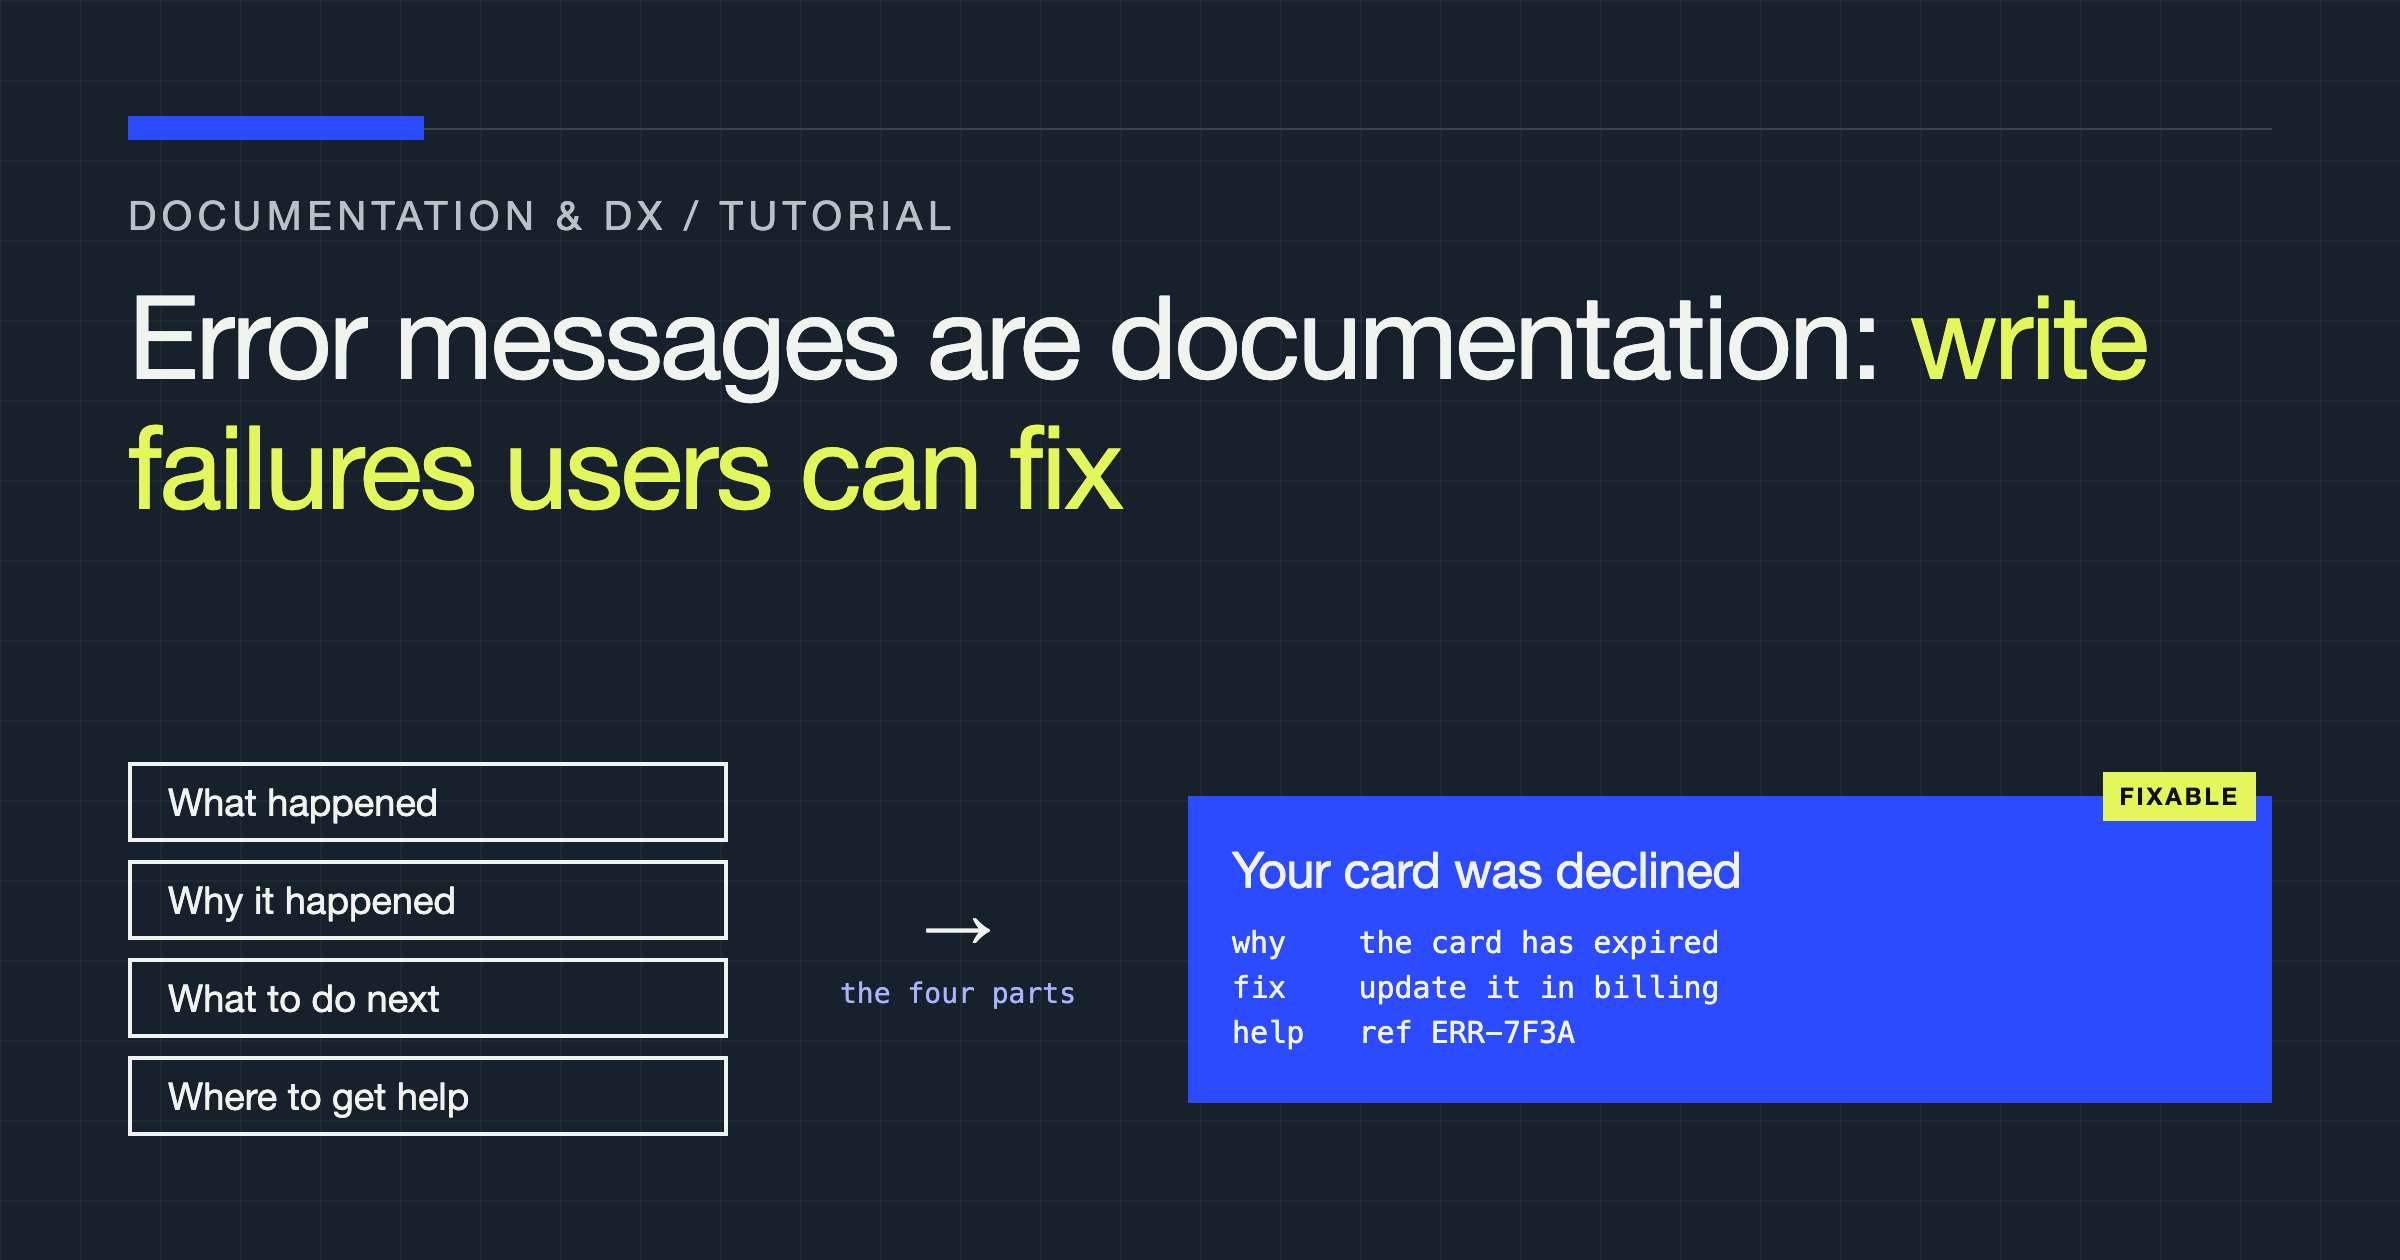
Error Messages Are Documentation: A Field Guide to Writing Failures Users Can Fix
A practical method for writing error messages that name the problem, state the cause, and hand the user a fix they can actually perform.
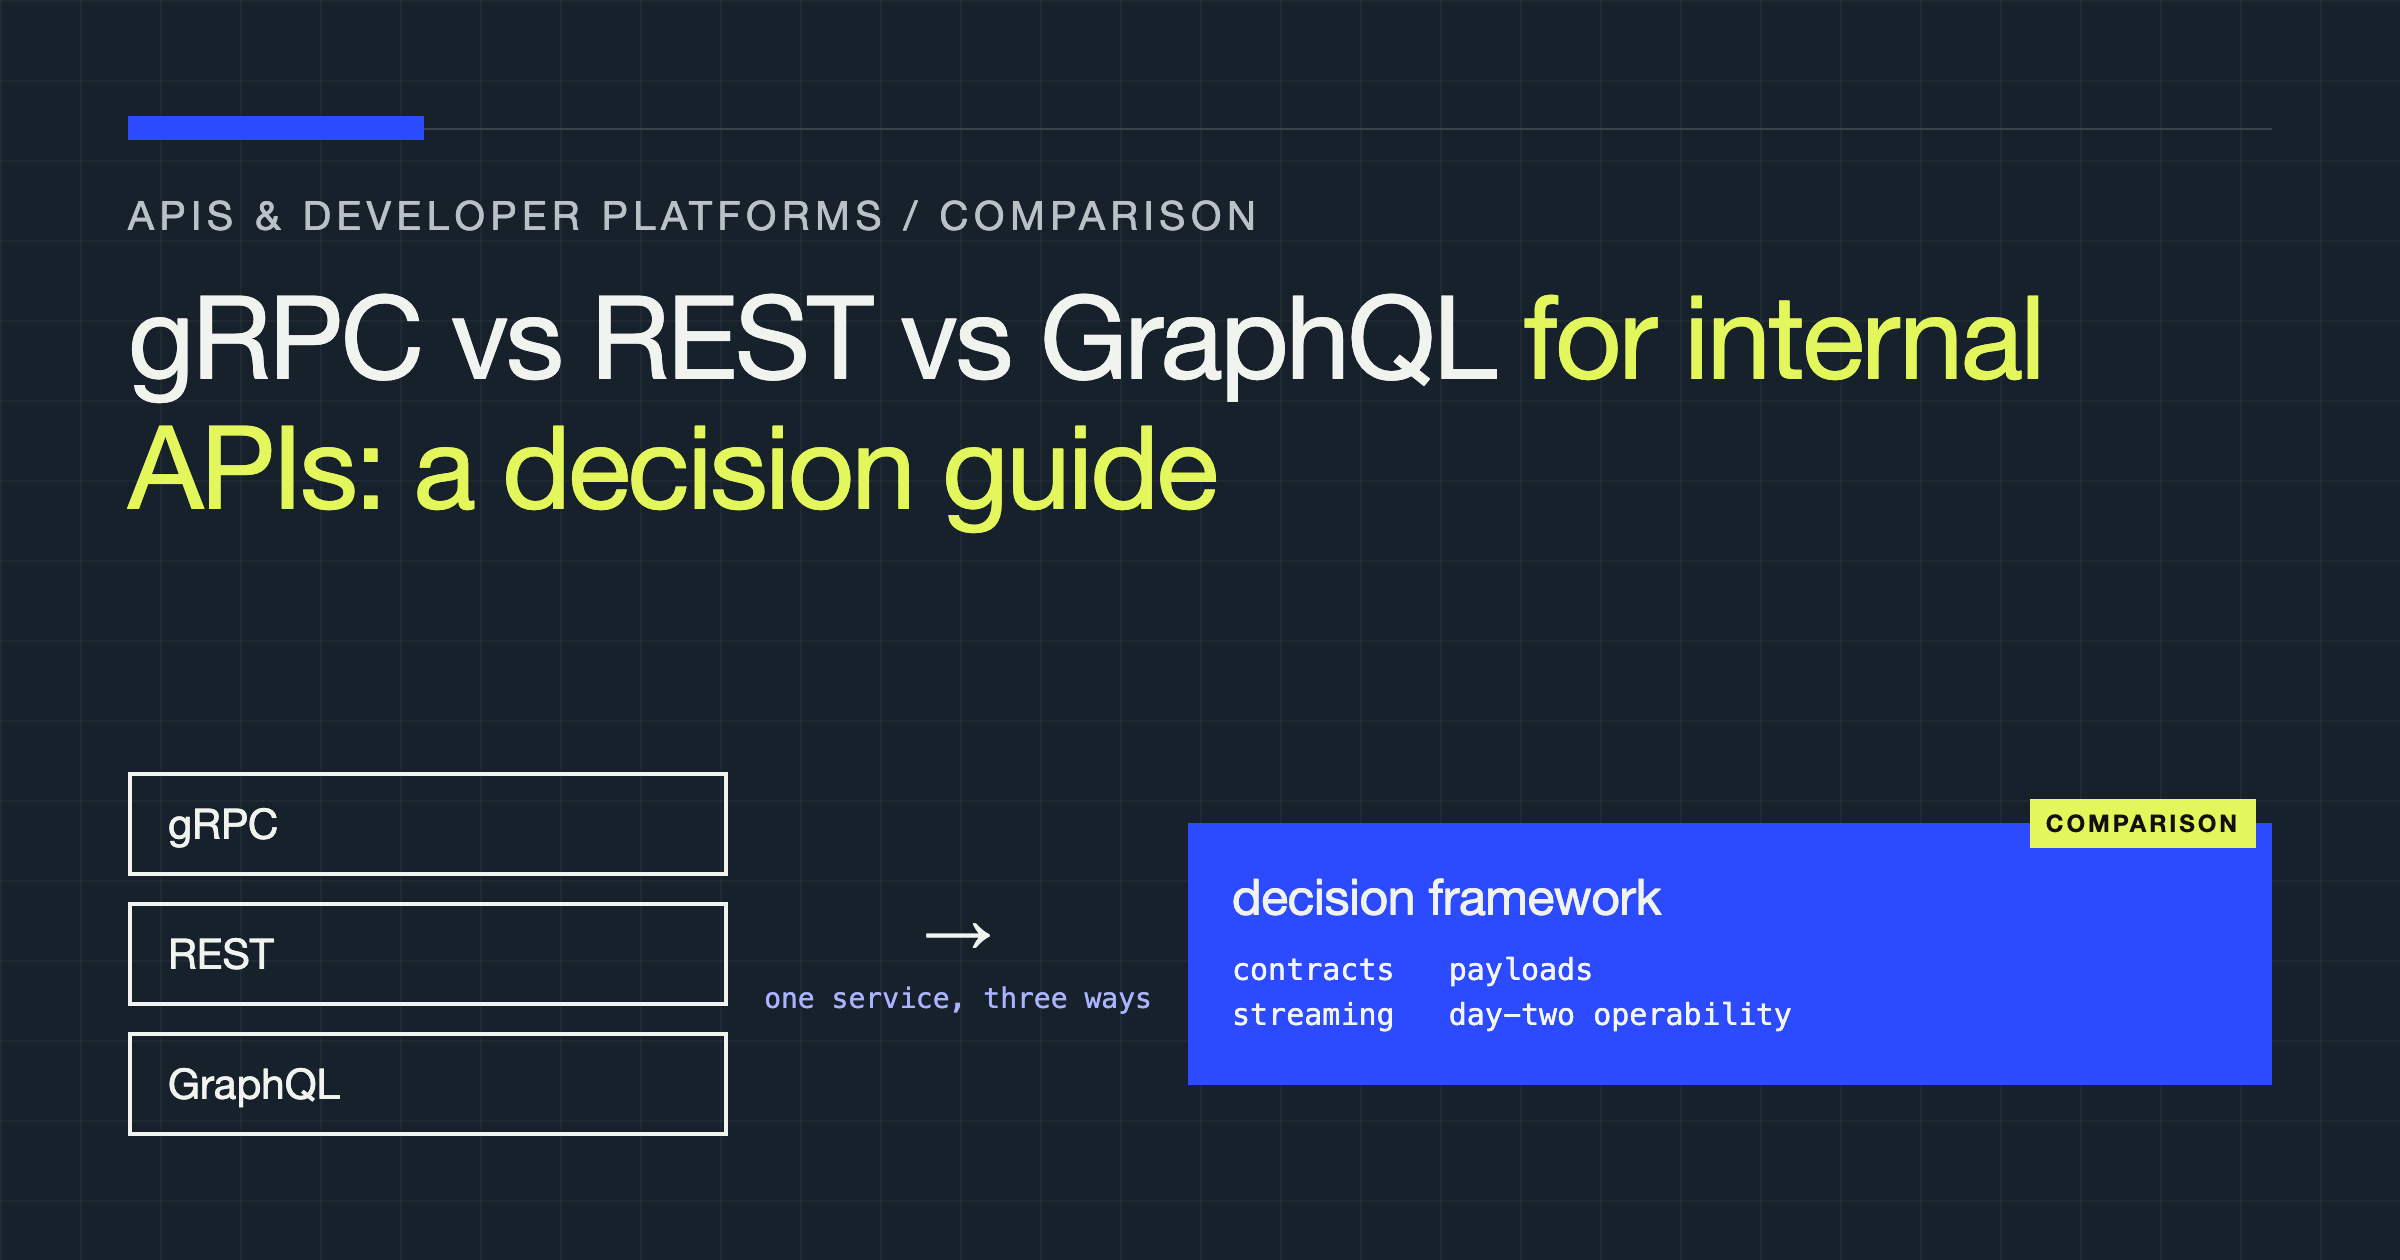
gRPC vs REST vs GraphQL for Internal APIs: A Decision Guide with Working Examples
The same internal service built three ways: compare gRPC, REST, and GraphQL on contracts, payloads, streaming, and operability, then decide with a framework you can reuse.
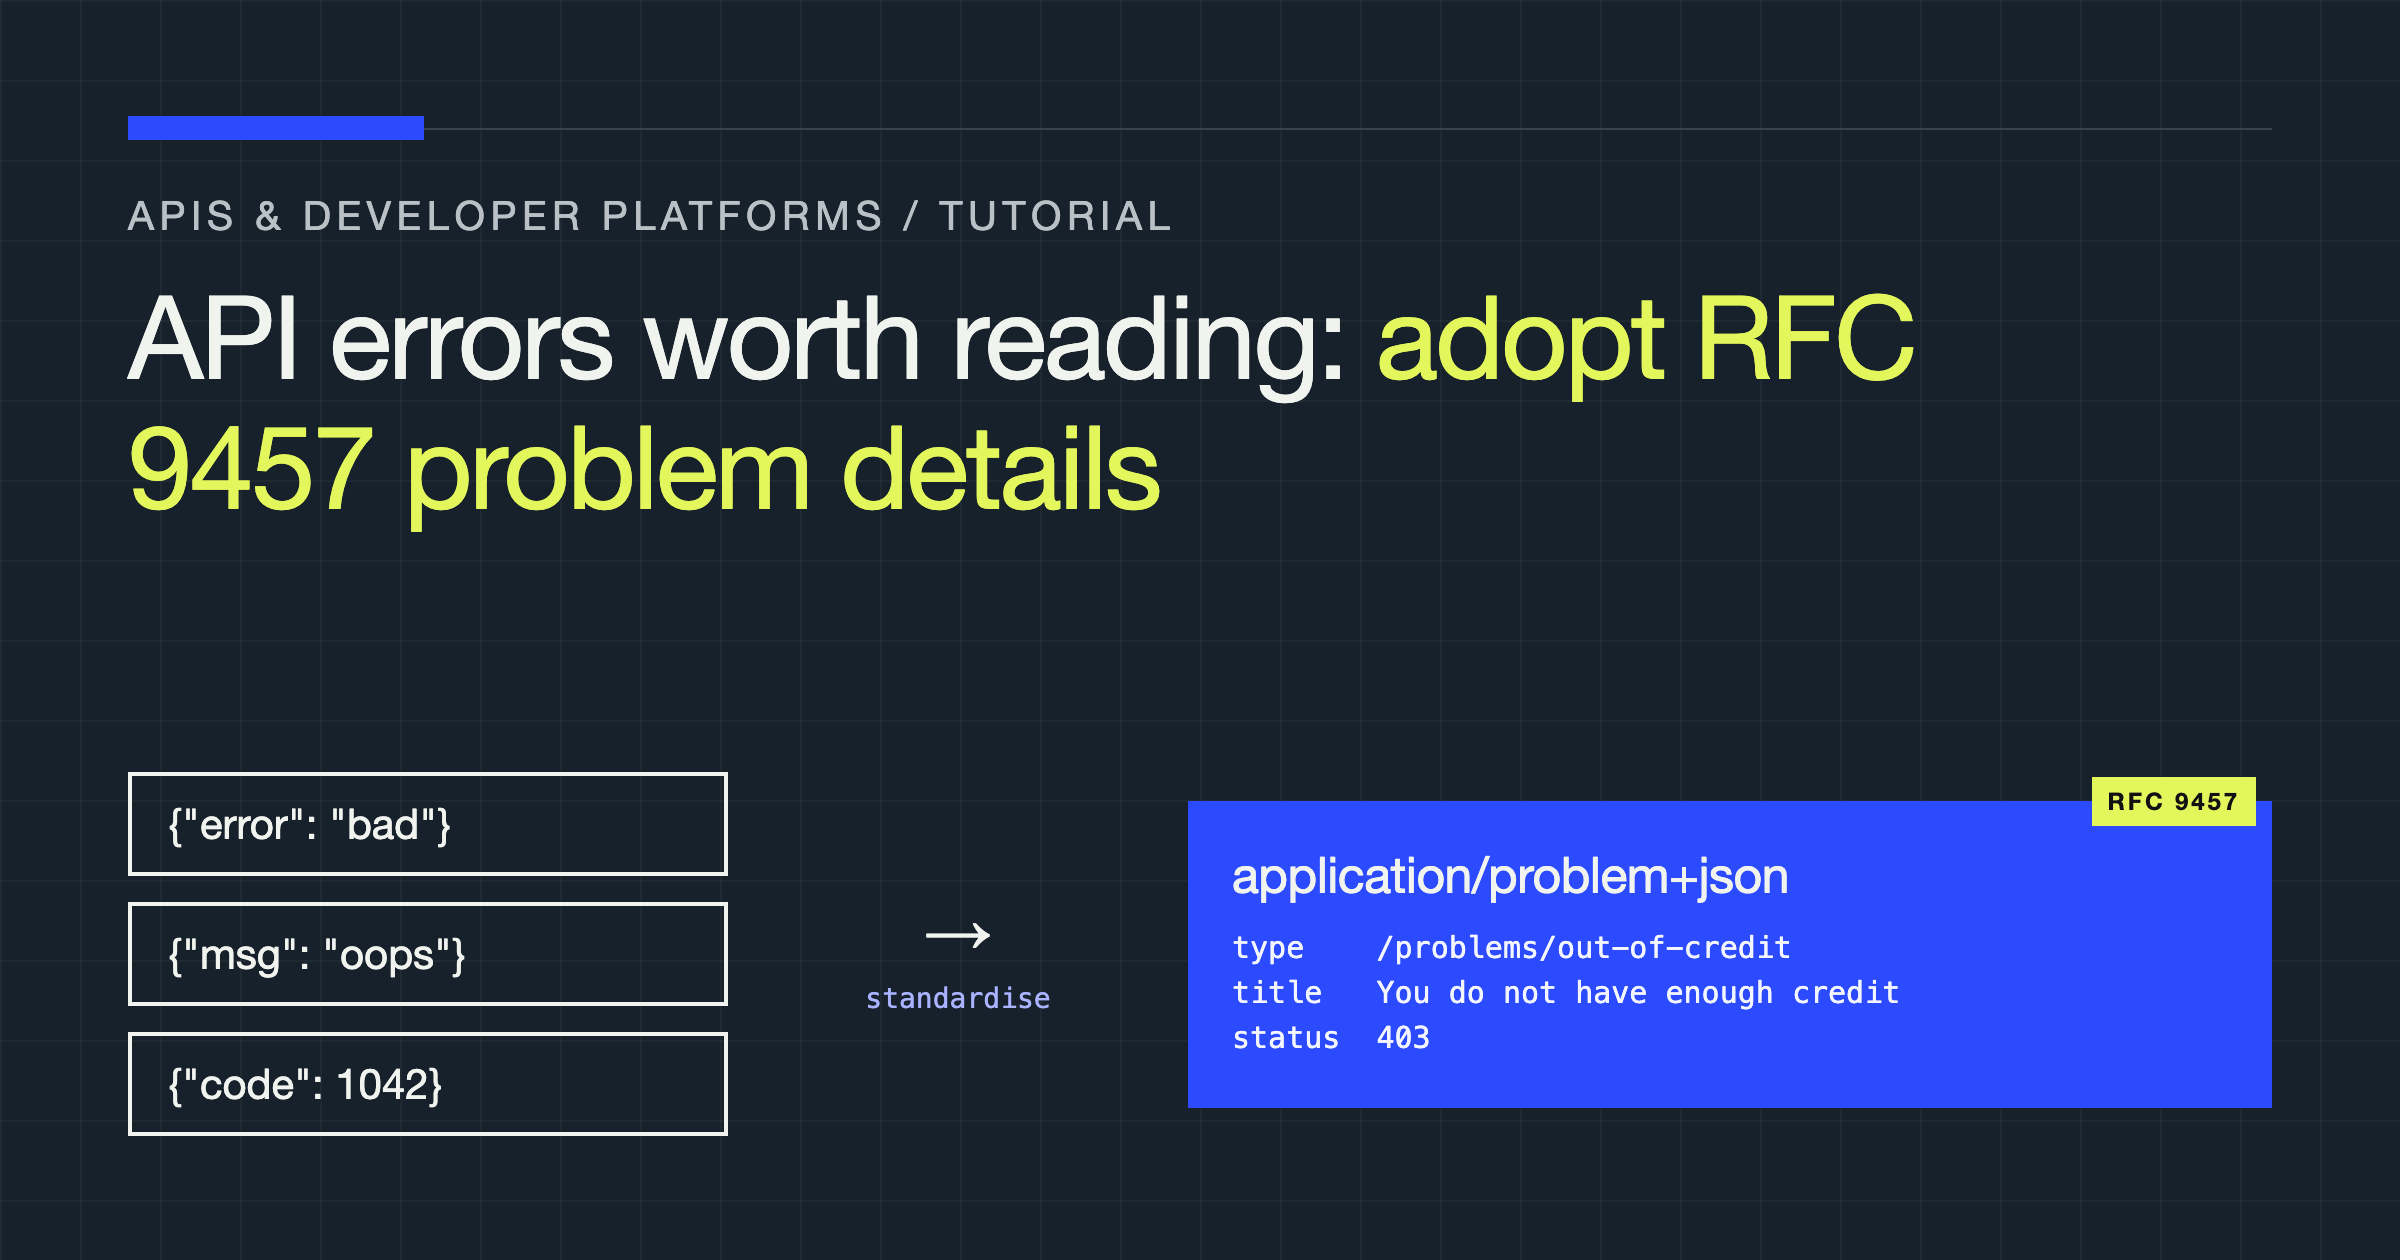
API Errors Worth Reading: Adopting RFC 9457 Problem Details
Replace ad-hoc error JSON with RFC 9457 problem details: a standard envelope, extension members for validation, and a migration path that keeps old clients working.
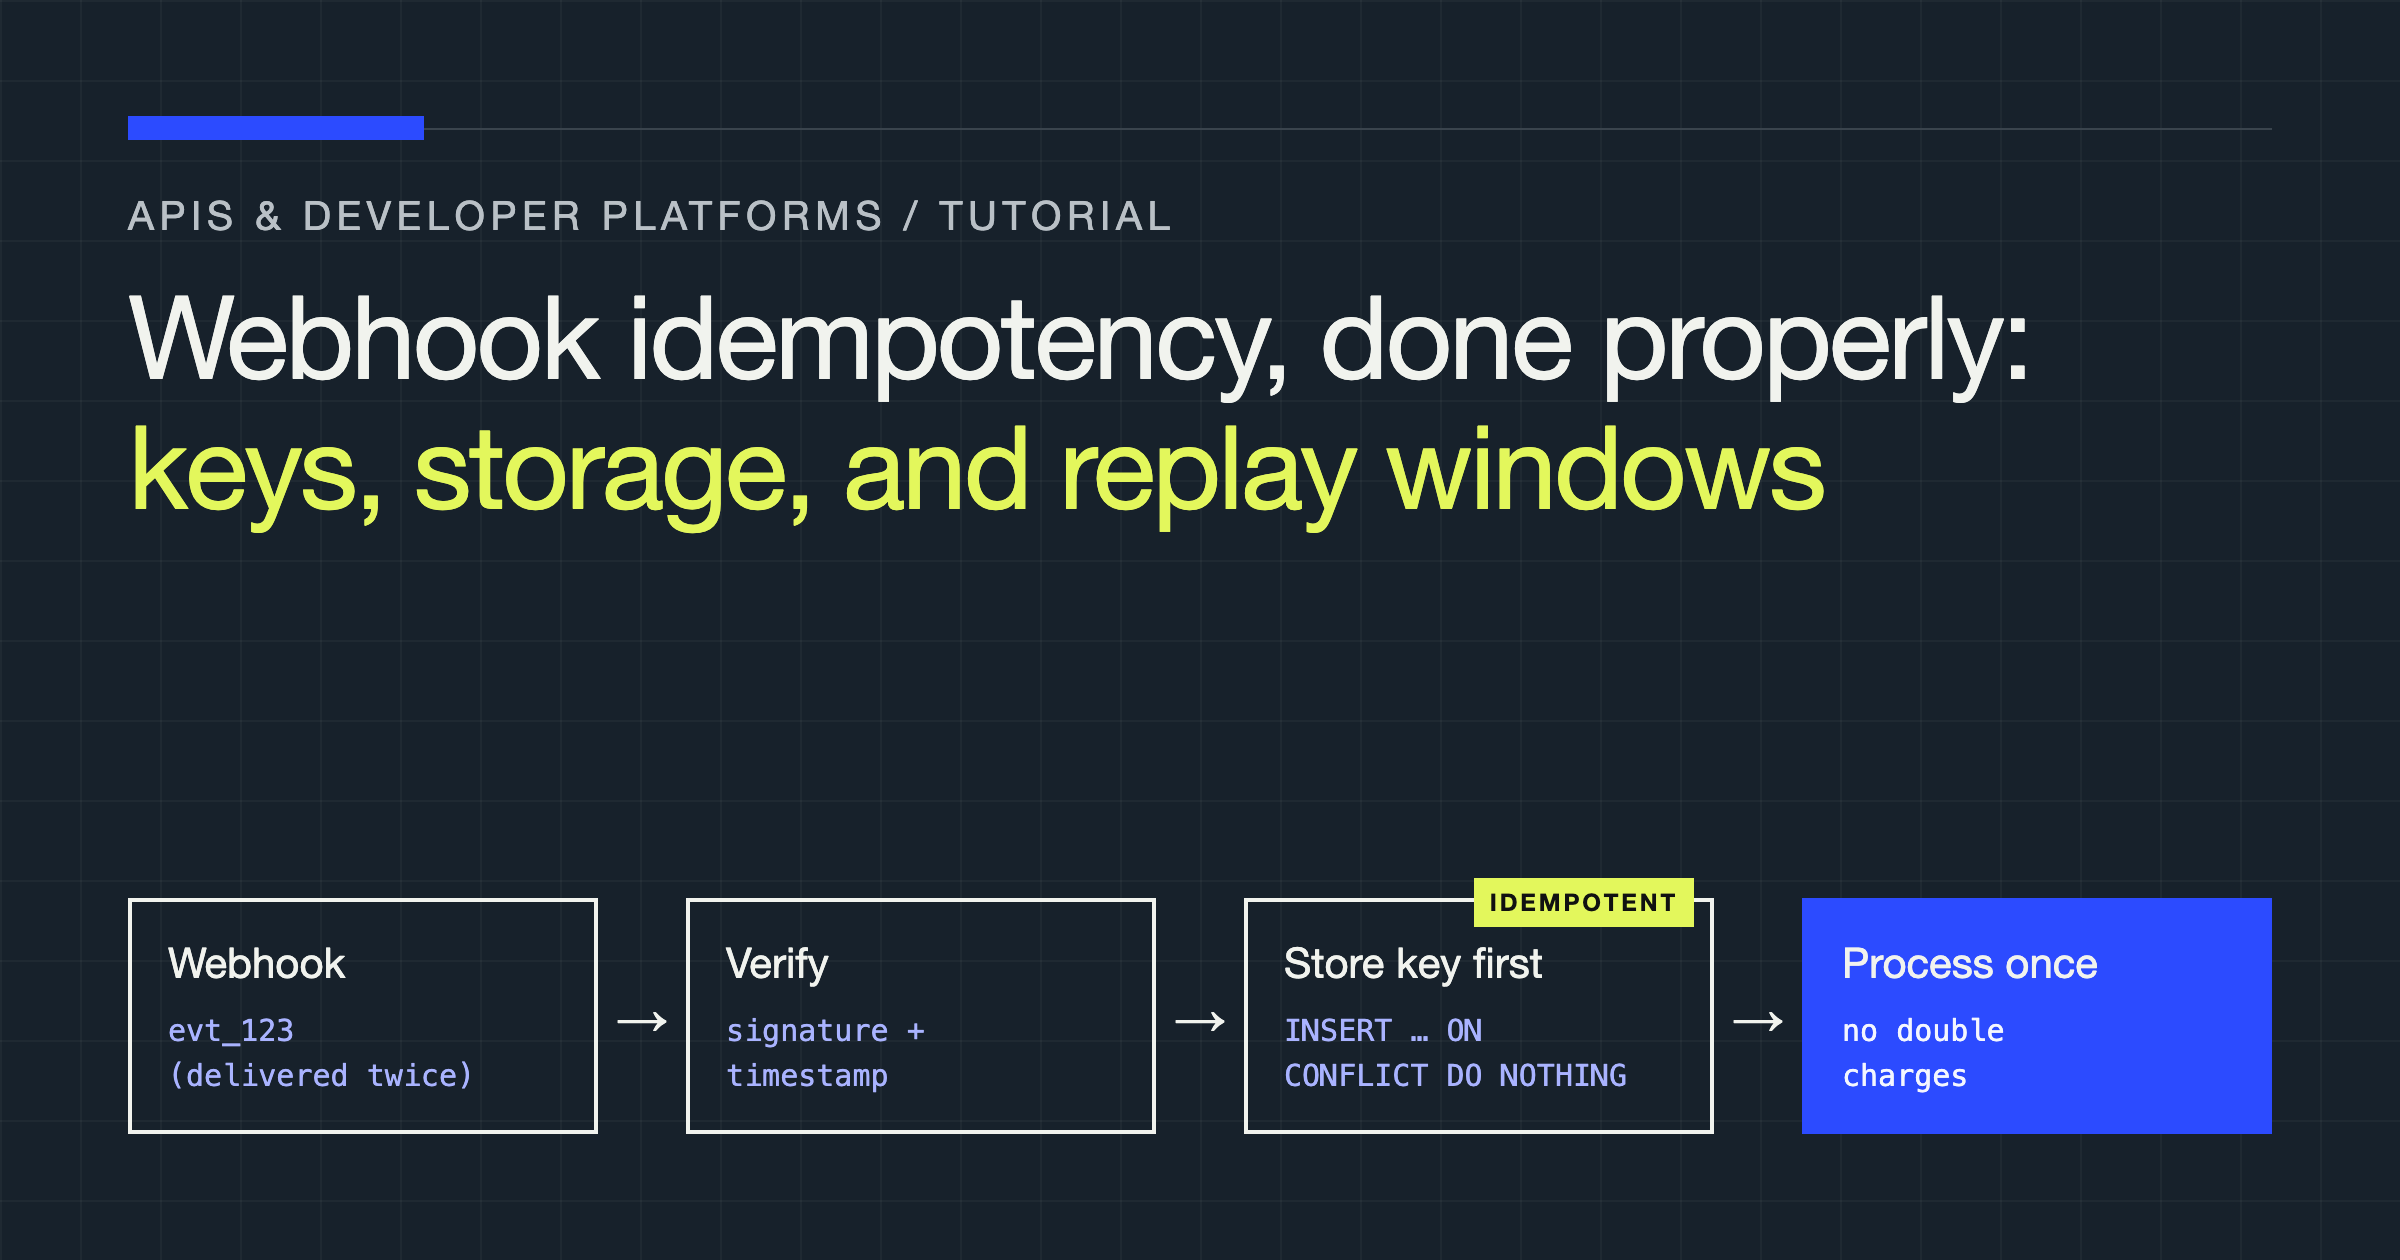
Webhook Idempotency, Done Properly: Keys, Storage, and Replay Windows
Build a webhook receiver that safely handles duplicates, retries, and replays without double-charging customers or corrupting state.
No matches in this set.
Clear a filter or try another combination.